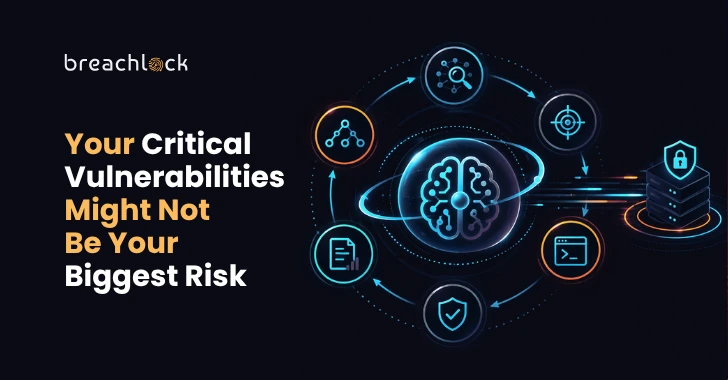
Severity Alone Does Not Represent Real-World Risk
A Critical vulnerability may look alarming in a vulnerability scanner report.
However, if the vulnerable system sits behind strong network segmentation, strict identity controls, and effective security defenses with no viable path to sensitive assets, its immediate business risk may be lower than the severity score suggests.
A Medium-severity vulnerability may represent a much greater risk when it exists on an internet-facing system and allows an attacker to:
- Establish an initial foothold;
- Obtain credentials;
- Escalate privileges;
- Move laterally;
- Chain additional weaknesses;
- Reach sensitive systems or data.
This demonstrates why vulnerability prioritization cannot rely on severity scores alone.
Autonomous Penetration Testing Adds Attack-Path Validation
A vulnerability scanner typically answers the question:
"What vulnerabilities exist?"
Autonomous Penetration Testing attempts to answer a different question:
"What can an attacker actually achieve using these vulnerabilities?"
Instead of evaluating individual findings in isolation, autonomous testing can determine whether a vulnerability:
- Can be reached;
- Can be successfully exploited;
- Can be chained with other weaknesses;
- Enables privilege escalation;
- Provides access to another system;
- Creates a viable route to a valuable target.
This process is known as attack-path validation.
Why Point-in-Time Penetration Testing Is No Longer Enough
Traditional penetration testing remains highly valuable because experienced pentesters can reason through complex attack scenarios.
Human experts can:
- Chain multiple vulnerabilities;
- Test business logic;
- Evaluate authentication and authorization;
- Identify privilege escalation opportunities;
- Determine whether theoretical weaknesses can lead to compromise.
The challenge is that modern environments change continuously.
After a penetration test is completed:
- Cloud infrastructure may be modified;
- New applications may be deployed;
- User identities may be created or removed;
- Configuration drift may occur;
- New assets may appear;
- Security controls may change;
- New vulnerabilities may emerge.
A penetration test may accurately describe the environment when it is performed, but that environment may look very different weeks or months later.
Continuous Penetration Testing
Autonomous Penetration Testing helps move security validation from periodic assessments toward continuous security validation.
Organizations can perform testing:
- On demand;
- After new deployments;
- After remediation;
- Following configuration changes;
- When new attack paths appear;
- When security controls need to be revalidated.
Continuous penetration testing is not simply about running vulnerability scanners more frequently.
It requires the ability to continuously perform meaningful offensive security testing and determine how far an attacker could actually progress through an environment.
Vulnerability Scanning vs. Autonomous Penetration Testing
Automated vulnerability scanning is primarily designed to identify known weaknesses.
Scanners can:
- Inspect assets;
- Match software against vulnerability databases;
- Detect known CVEs;
- Identify configuration changes;
- Generate remediation lists.
But detecting a vulnerability is different from demonstrating that an attacker can exploit it.
Autonomous Penetration Testing can go further by performing activities such as:
- Reconnaissance;
- Identifying attack opportunities;
- Attempting exploitation;
- Testing authentication and authorization;
- Chaining multiple weaknesses;
- Pivoting across systems;
- Performing lateral movement;
- Pursuing a defined attack objective.
In simple terms:
Automated scanning identifies possibilities. Autonomous penetration testing produces evidence.
AI Is Changing Penetration Testing
One of the most significant developments in autonomous penetration testing is not simply the automation of individual tasks.
Modern systems are increasingly capable of reasoning through multi-step attack scenarios.
Rather than stopping after finding an individual vulnerability, an autonomous system can evaluate how multiple weaknesses interact and determine whether they form a viable path to compromise.
An attack path might look like:
Initial Access → Privilege Escalation → Lateral Movement → Sensitive Asset Access
This allows security teams to move beyond isolated findings and understand the full sequence an attacker may use to reach a meaningful objective.
From Vulnerability Lists to Evidence of Compromise
One of the biggest challenges in vulnerability management is volume.
Large organizations may have thousands of vulnerability findings while remediation resources remain limited.
Attack-path validation helps security teams prioritize vulnerabilities that:
- Are actually exploitable;
- Can be chained with other weaknesses;
- Enable privilege escalation;
- Allow lateral movement;
- Provide access to sensitive systems or data.
This enables remediation decisions to focus on real exploitability and business impact, rather than relying entirely on severity ratings.
Autonomous Testing Still Requires Human Judgment
Autonomous execution does not eliminate the need for human security professionals.
Technology can perform tasks such as:
- Discovering attack paths;
- Testing exploits;
- Repeating attack scenarios;
- Generating evidence;
- Testing environments at scale.
However, human experts still need to determine:
- Which attack path creates the greatest business risk;
- Which remediation effort should take priority;
- Which operational constraints must be considered;
- Which regulatory requirements apply;
- What level of residual risk is acceptable;
- When deeper expert-led testing is required.
The objective of autonomous security testing is therefore not to remove humans from penetration testing.
Instead, automation can handle activities that machines can perform continuously at scale, while human expertise remains focused on decisions that require business context, judgment, and accountability.
The Future of Penetration Testing Is Continuous and Attack-Path Focused
The cybersecurity industry is gradually moving away from asking:
"How many vulnerabilities do we have?"
and toward asking:
"Which vulnerabilities create a credible path to compromise?"
In modern cloud, SaaS, hybrid, and rapidly changing environments, vulnerability severity represents only one part of the overall risk picture.
Continuous security validation combined with Autonomous Penetration Testing can help organizations continuously determine:
- Which systems can actually be compromised;
- Which security controls are working;
- Which attack paths currently exist;
- Which remediation actions will have the greatest impact.
Ultimately, the vulnerability with the highest severity score may not be the organization's biggest risk. The greatest risk may instead be a chain of smaller weaknesses that together create a complete path to a critical asset.
Leave a Comment